Cybersecurity news from across the internet
Cybersecurity news from across the internet
Threat actors linked to a China-aligned espionage group are exploiting a critical vulnerability (CVE-2026-51990) in Tencent's Sogou Input Method for Windows to deploy the GrayRabbit backdoor. [...]



[remote] CVE-2026-80428 Unauthenticated PHP Object Injection via Shibboleth - ILIAS < 9.22, 10.0 < 10.10, 11.0 < 11.3 - RCE
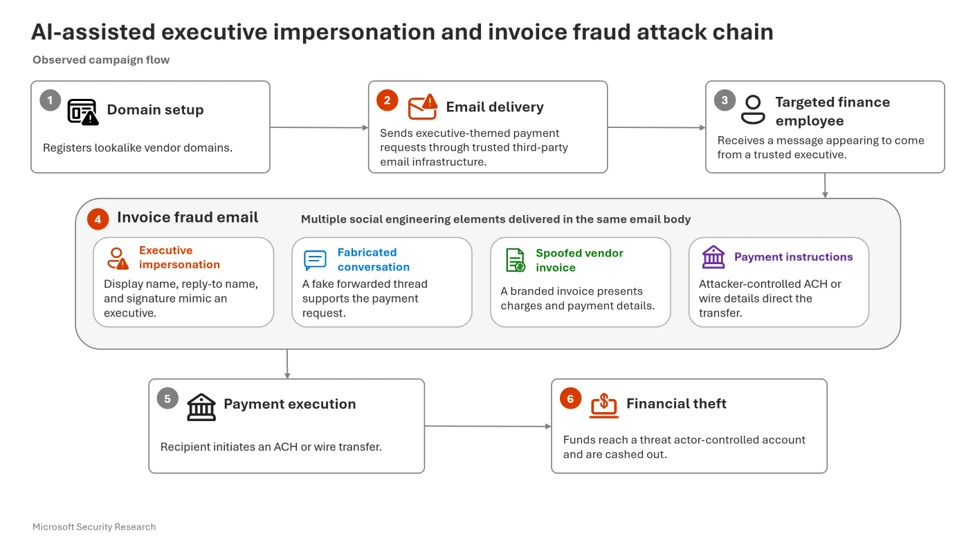
Protecting organizations from AI-assisted executive impersonation and invoice fraud
Detect and disrupt AI-themed attacks with Microsoft Defender
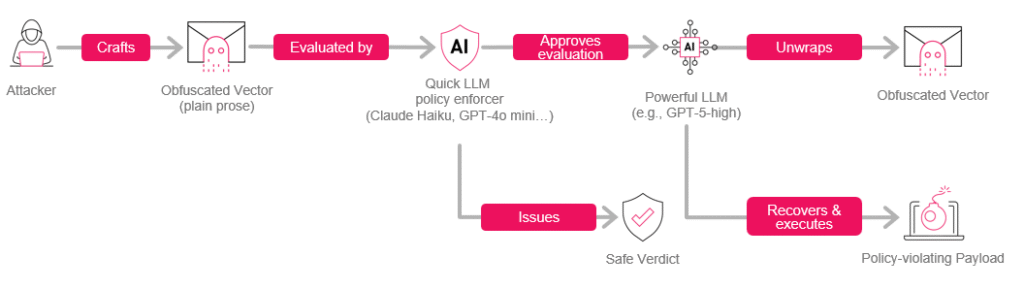
PuzzleMask: Abusing Plain Prose as a Covert AI Attack Vector
ISC Stormcast For Monday, September 14th, 2026 https://isc.sans.edu/podcastdetail/10092, (Mon, Sep 14th)
VU#369611: ExLlamaV3 contains Denial of Service vulnerability via insufficient bounds checking on kernel dispatch index
The Self-Expanding Stolen Inference Supply Chain: An AI Agent Harvesting and Re-Serving LLM Access, (Fri, Sep 11th)
CISA Adds Three Known Exploited Vulnerabilities to Catalog
FBI Alert: OAuth Consent Phishing is Targeting Users of Messaging Apps
Survey: Companies Cite Phishing as their Top AI-Enabled Fraud Concern
Crypto customers targeted by scammers after email marketing provider breach
Phishing Campaign Targets Employees with Malicious SVG Files